How to Protect Your WordPress Website From Brute Force Attacks
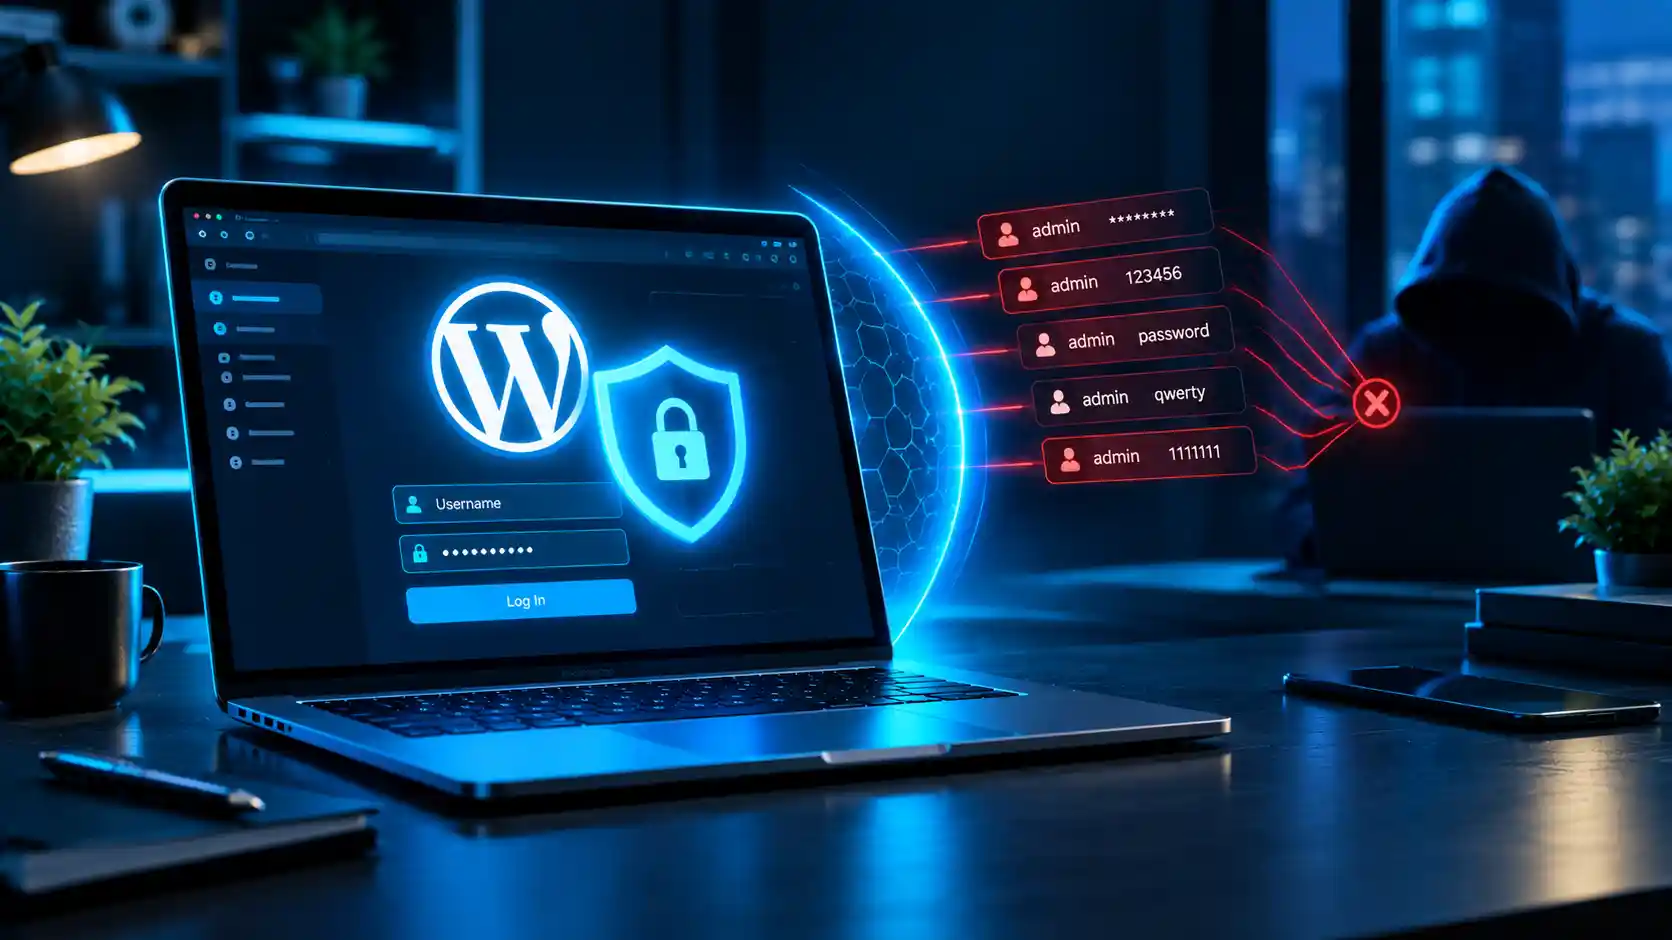
If you want to prevent WordPress brute force attacks, you need to understand how they work first. A brute force attack is simple in concept: a bot repeatedly guesses usernames and passwords on your login page until one combination works.
It’s not glamorous hacking. It’s automated, relentless, and surprisingly effective against sites with weak login security. The good news is that stopping it doesn’t require advanced technical skills, just a few deliberate changes.
What Is a Brute Force Attack?
A brute force attack works by systematically trying different username and password combinations against your login page. According to OWASP, this method relies on predetermined values submitted repeatedly to a server, with the attacker analyzing each response to see if it succeeded.
On WordPress specifically, the default login page is well known, which makes it an easy target for automated bots scanning thousands of sites at once.
Why WordPress Sites Are Common Targets
WordPress runs a large share of websites worldwide, so bots are built specifically to target it. Attackers don’t usually pick your site on purpose. They scan broadly, looking for:
- Weak or reused passwords
- The default “admin” username
- No login attempt limits
- Outdated security plugins or none at all
If your site matches these patterns, it becomes an easy target regardless of its size or traffic.
How to Prevent WordPress Brute Force Attacks
1. Use Strong, Unique Passwords
This is the single most effective step to prevent WordPress brute force attacks. A long, random password with a mix of characters takes dramatically longer to guess than a short or common one.
- Use a password manager to generate and store passwords.
- Never reuse passwords across sites.
- Avoid predictable patterns like names, birthdays, or “password123.”
2. Remove or Rename the “Admin” Username
If your admin account is still named “admin,” change it. Attackers assume this username exists on most WordPress sites, so removing it eliminates half their guessing work immediately.
3. Limit Login Attempts
Limiting how many times someone can try to log in before being temporarily blocked stops brute force bots cold. Most security plugins include this feature, and some hosting providers offer it at the server level too.
4. Enable Two-Factor Authentication
Two-factor authentication (2FA) adds a second verification step beyond the password, usually a code from an app or SMS. Even if an attacker guesses your password correctly, they still can’t log in without that second code.
5. Add a Firewall
A web application firewall filters malicious traffic before it ever reaches your login page. Many security plugins include a basic firewall, and some hosting companies provide one at the server level for extra protection.
6. Change the Default Login URL
Moving your login page away from the standard /wp-login.php address hides it from bots that scan for that specific path. This isn’t a complete defense on its own, but it does reduce automated login attempts significantly.
7. Keep WordPress, Themes, and Plugins Updated
Outdated software sometimes contains known vulnerabilities that go beyond simple password guessing. Regular updates close those gaps and support your broader effort to prevent WordPress brute force attacks.
Signs Your Site Might Be Under Attack
Watch for these warning signs:
- A sudden spike in failed login attempts
- Unusual server resource usage or slow loading times
- Unfamiliar admin accounts appearing in your user list
- Security plugin alerts about repeated login failures from the same IP ranges
Most hosting dashboards and security plugins log this activity, so check them periodically rather than waiting for something to go visibly wrong.
What to Do If an Attack Is Already Happening
If you notice active brute force attempts:
- Change all admin passwords immediately.
- Enable or tighten login attempt limits.
- Review your user list for unauthorized accounts.
- Check your firewall or security plugin logs for the source IPs.
- Consider temporarily blocking suspicious IP ranges if the activity continues.
Acting quickly reduces the chance that repeated guessing eventually succeeds.
Building Long-Term Login Security
Preventing brute force attacks isn’t a one-time setup. Treat it as an ongoing part of your site’s maintenance routine:
- Review login logs monthly.
- Update passwords periodically, especially for shared or client accounts.
- Reassess user roles and remove accounts no longer in use.
- Keep your firewall and security plugin settings current as new threats emerge.
Conclusion
To prevent WordPress brute force attacks, focus on the basics first: strong passwords, limited login attempts, two-factor authentication, and a firewall. These steps address the vast majority of automated attacks without requiring constant manual monitoring.
Security isn’t about eliminating every possible risk. It’s about making your site a difficult, unattractive target, so bots move on to easier ones.
If managing all of this yourself feels like too much, working with professional WordPress security services can save time and ensure these protections are set up correctly from the start.